Public recovery record
Wallet incident & NFT recovery
My account of the 31 October 2026 malware and wallet incident: how it happened, the evidence retained, the recovery process and the individually documented NFTs.
Last updated:
01 / SCOPE & RECORDS
The full scope, with the gaps made clear
≈189 NFTs
Owner-reported overall estimate
109 NFTs
Individually itemized in the supplemental schedule
28 Ethereum · 81 Robinhood
Across 33 collections
I report approximately 189 affected NFTs overall. The available 5 November supplemental schedule identifies 109 distinct NFTs by chain, contract and token ID. The remaining portion of the estimate is not itemized in the records reviewed for this page; it is not presented as verified loss. No aggregate monetary valuation is asserted.
The support draft also mentions 87 historical NFT receipt records across three additional wallets. Those records are explicitly marked NOT confirmed stolen, and no 31 October outgoing NFT events were found for those wallets in that review. They are excluded from this register and must not be added to the 109 as confirmed thefts.
View all 109 documented NFTs →Separate purchase register with collection, chain, exact token ID, full OpenSea link and transaction evidence.02 / SUITED APE SOCIETY · ROBINHOOD CHAIN
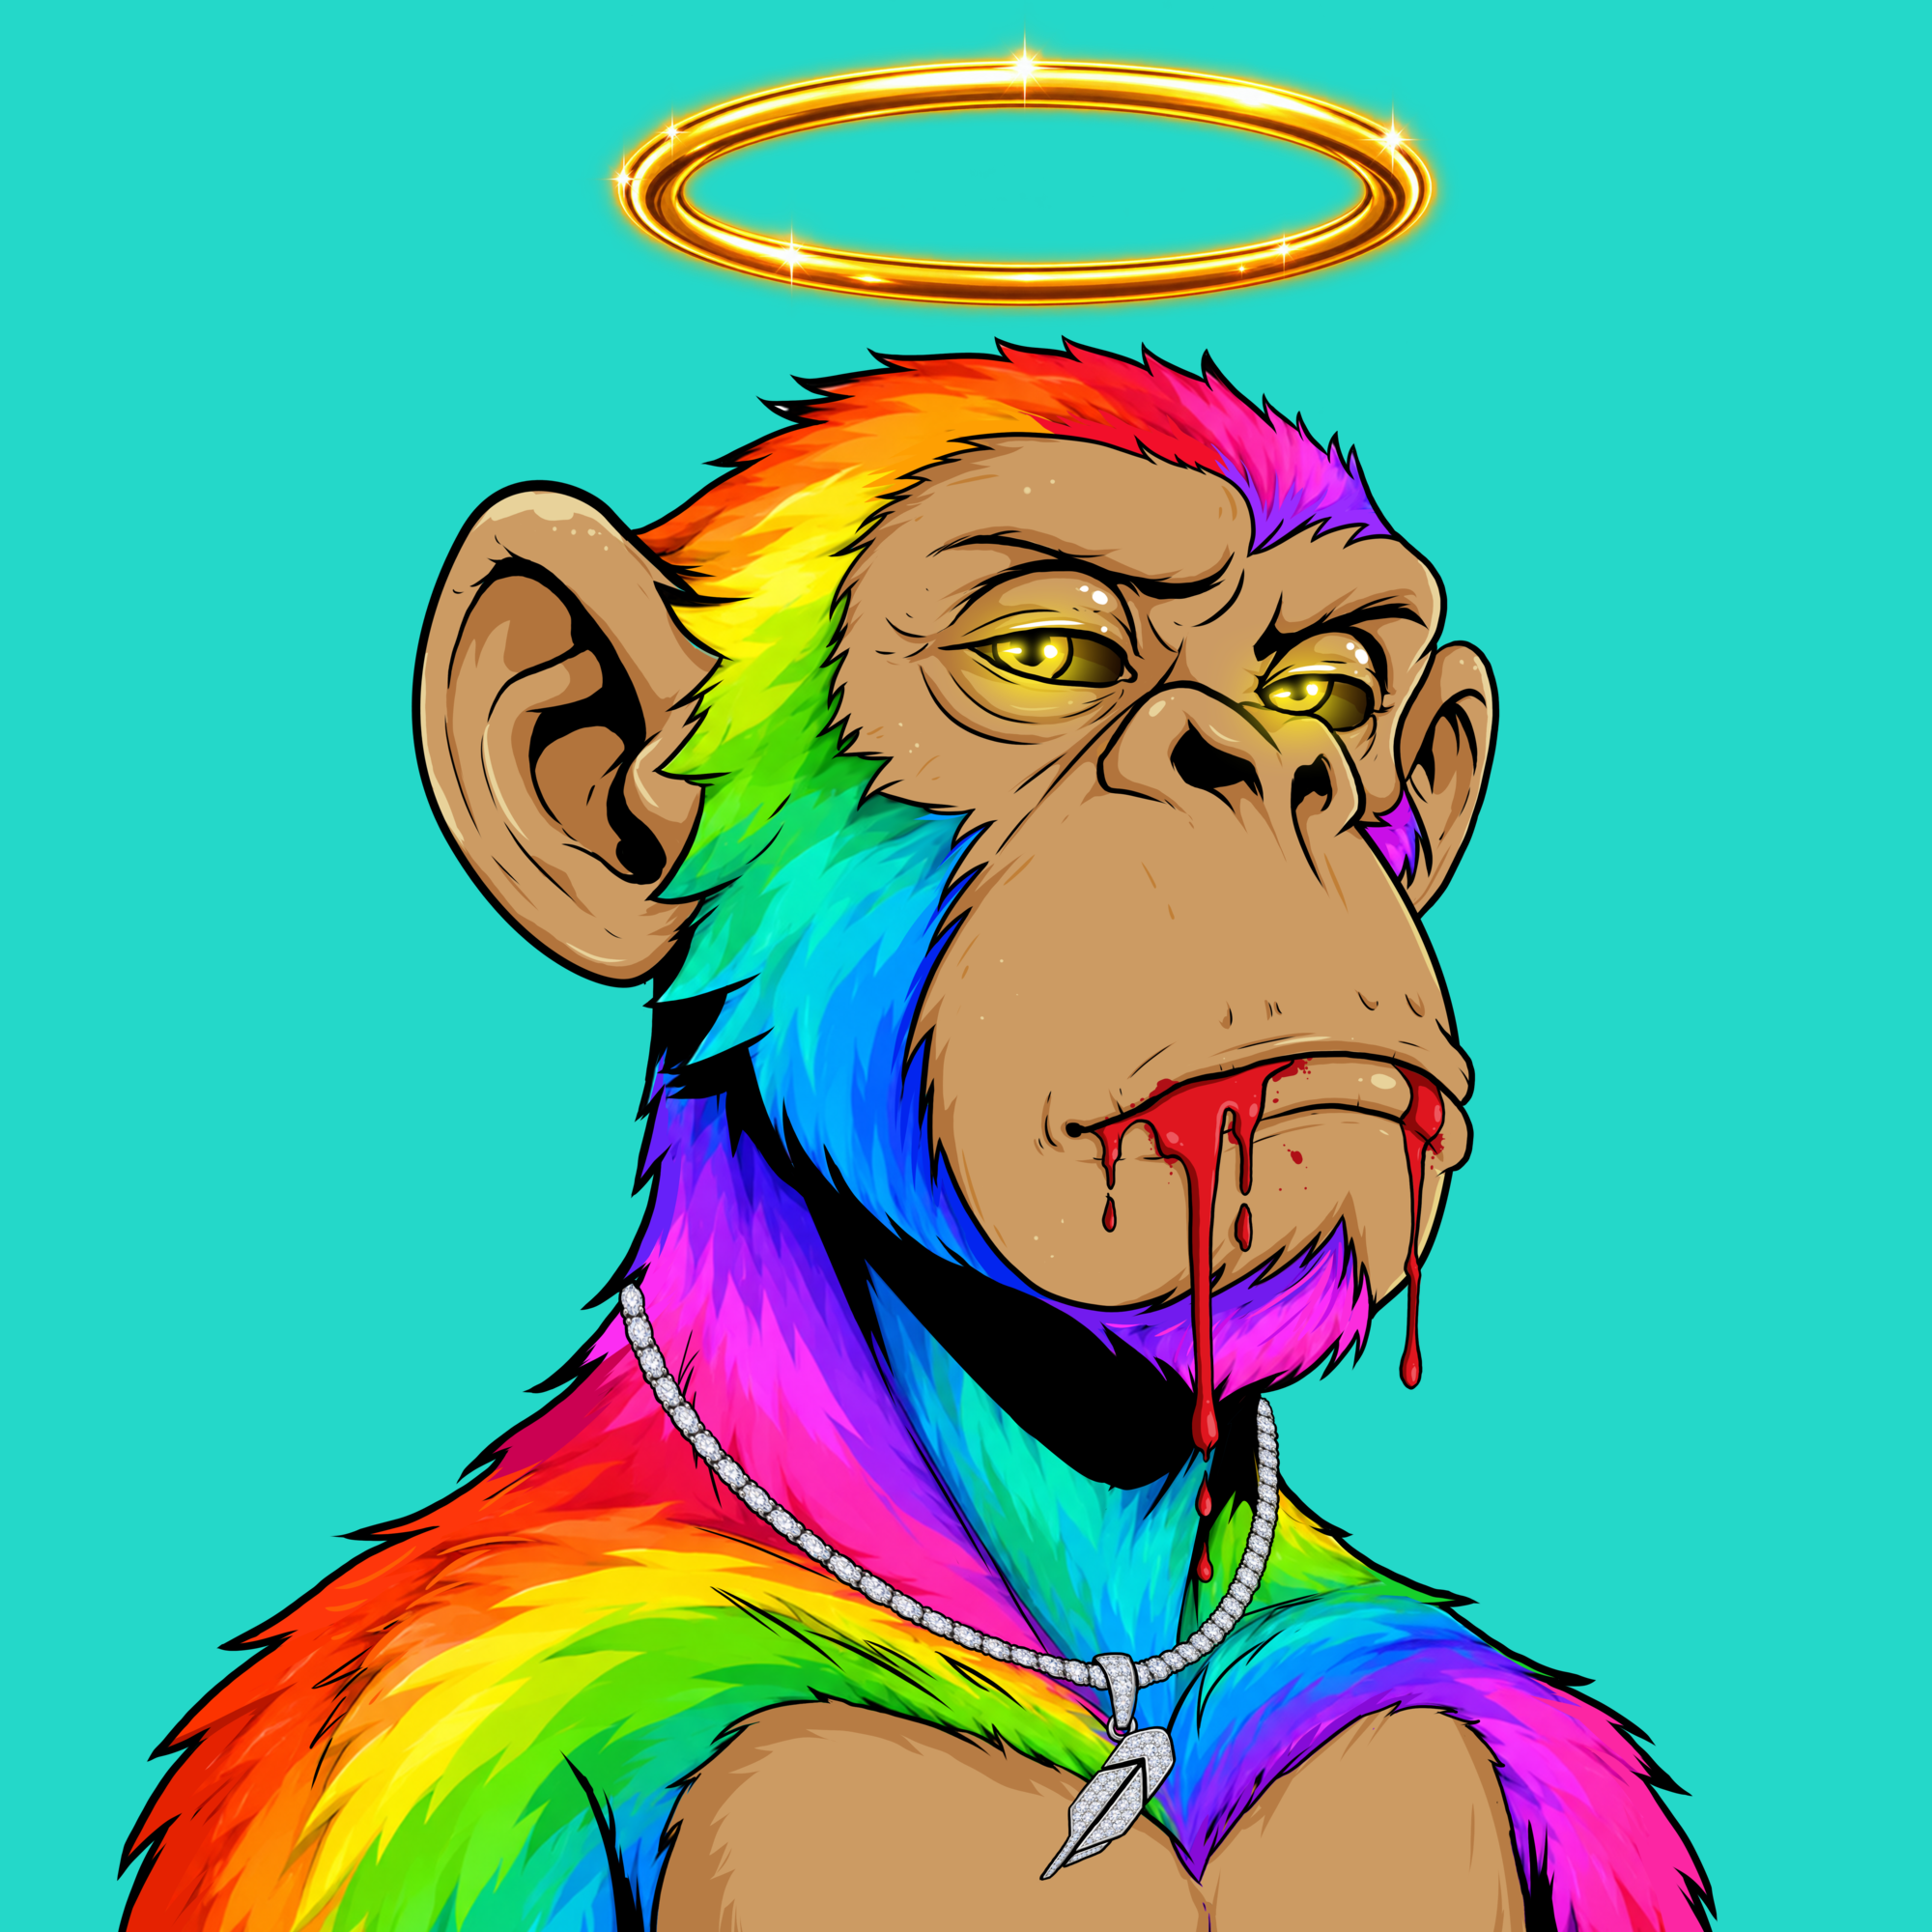
Two of the affected NFTs
https://opensea.io/item/robinhood/0xe638f58c87258ece6c0eddc46f70327663635c69/1648
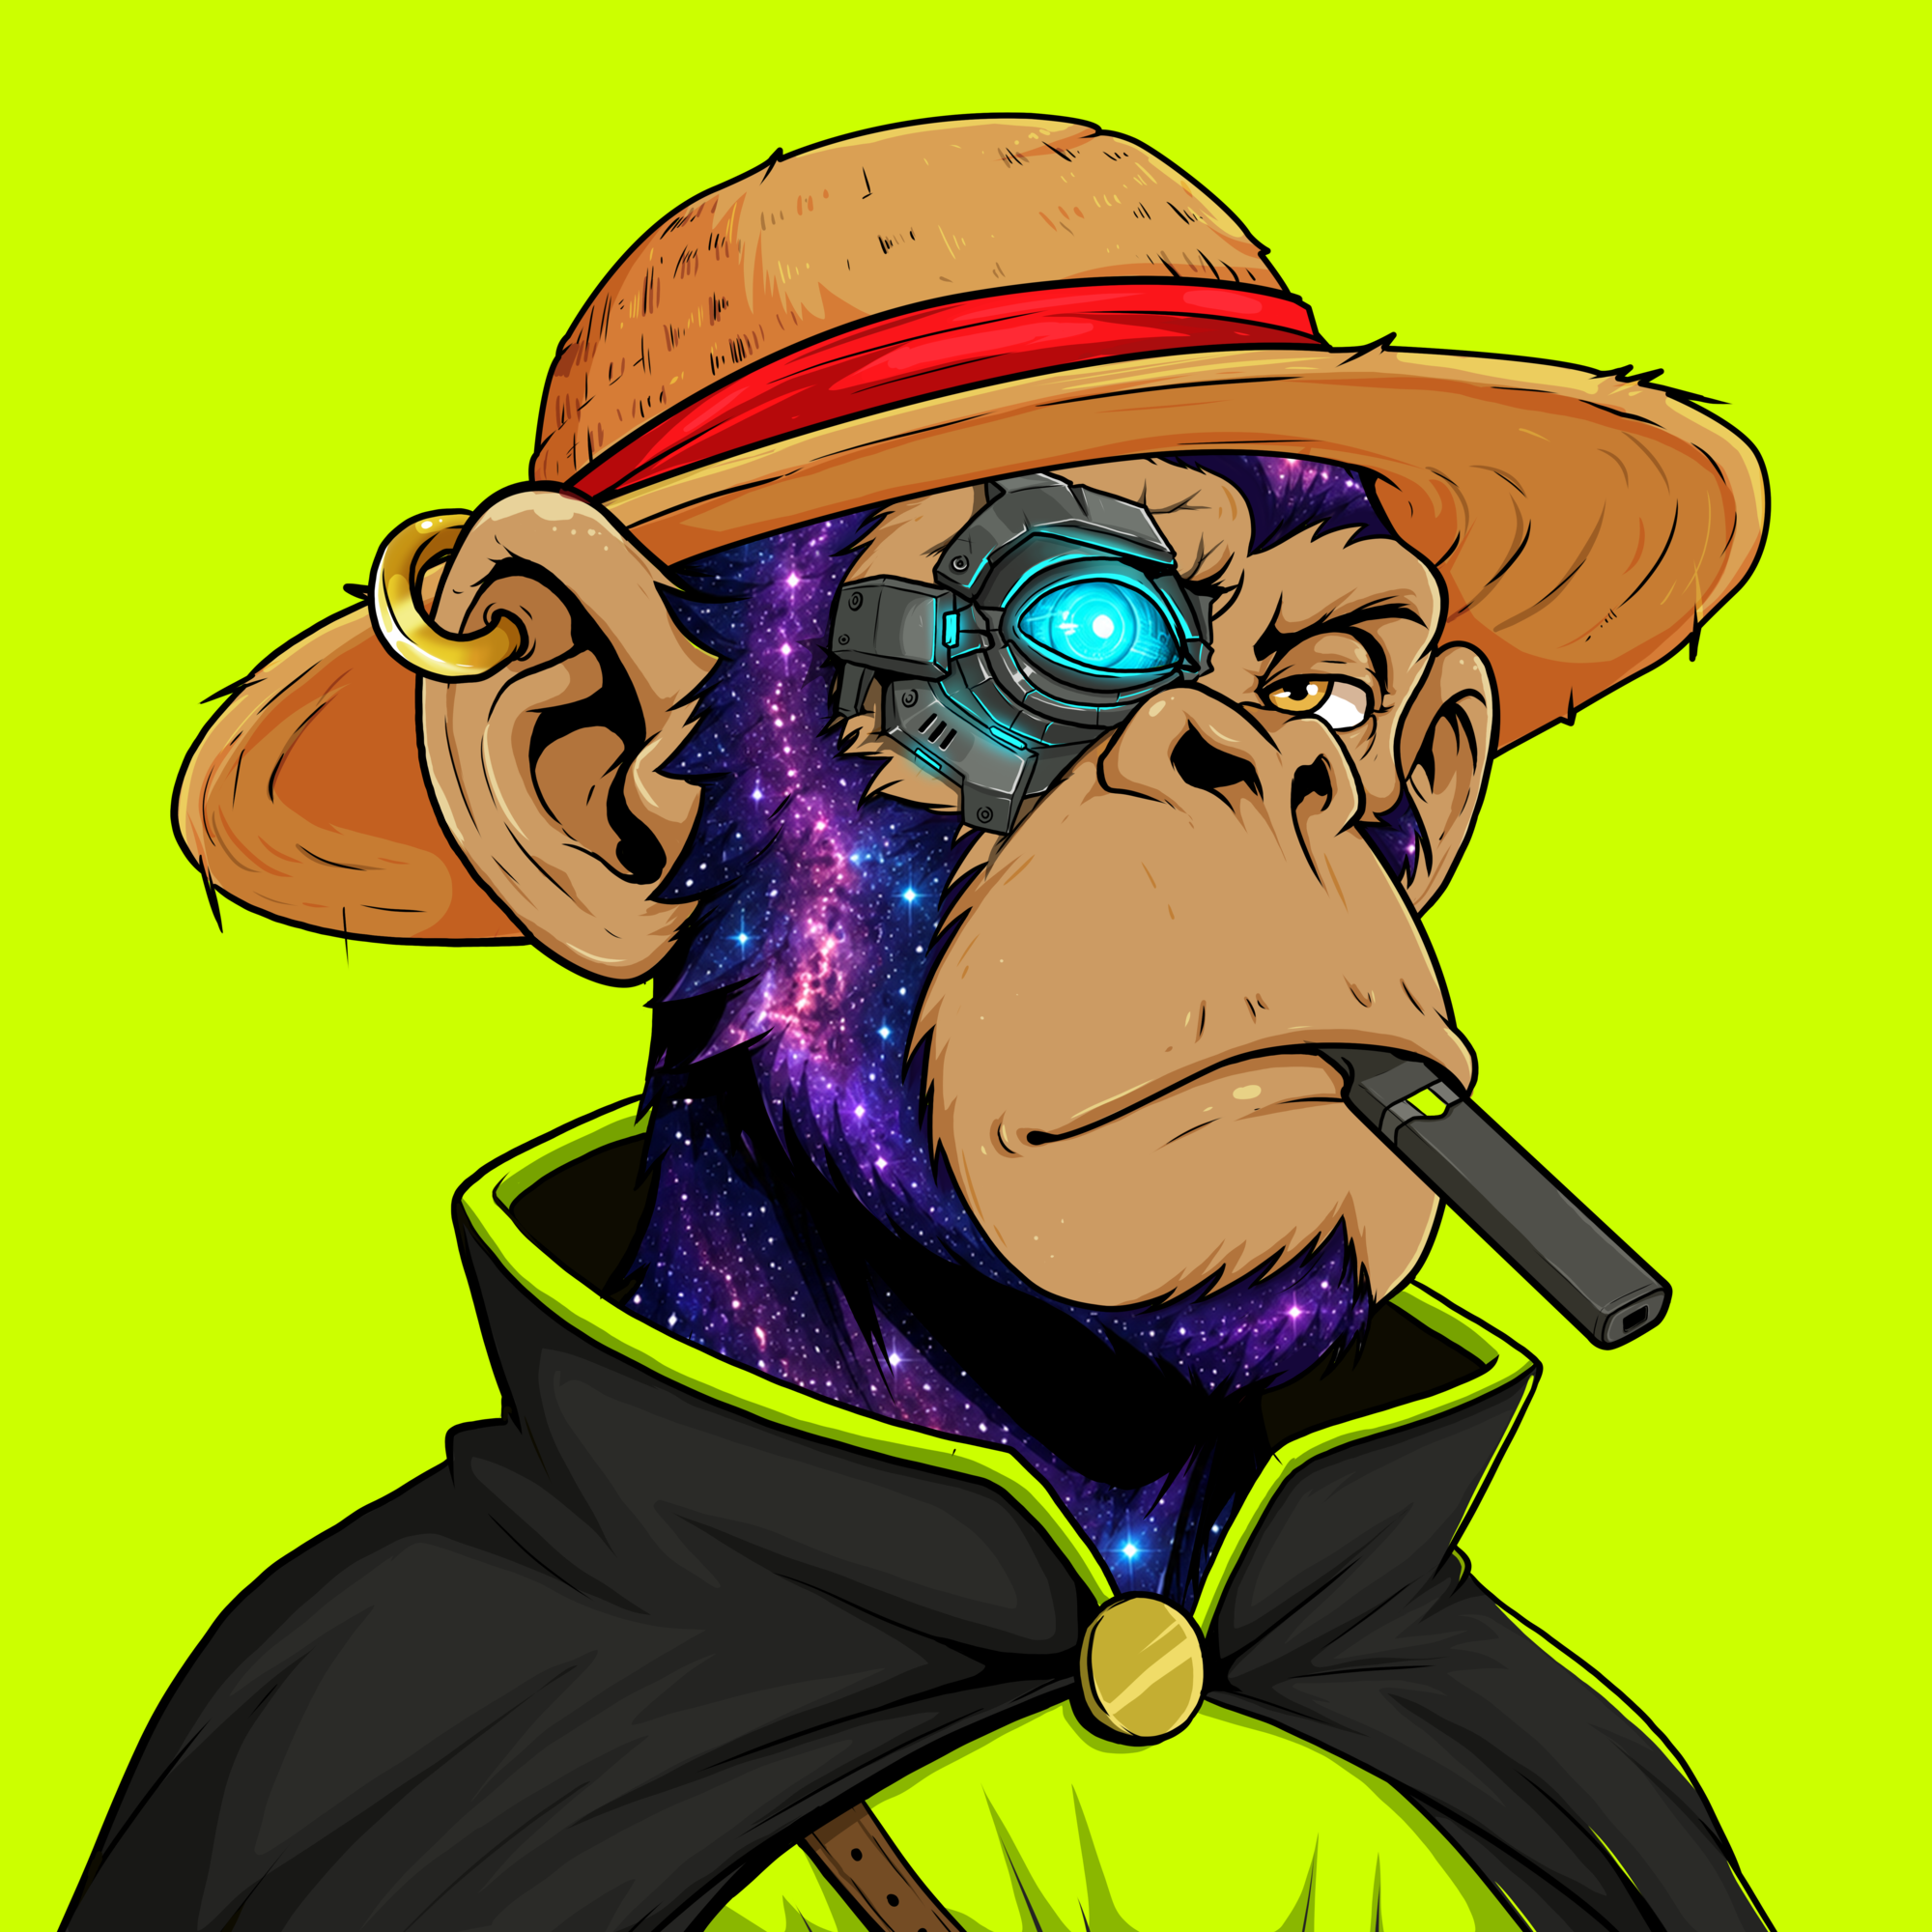
Ape #1858
Reported stolenArtwork: Suited Ape Society. Item links identify the reported assets; they do not identify an attacker.
03 / HOW IT HAPPENED
A fake invitation led to device compromise
The approach began as a podcast invitation about Mintropolis. A fraudulent page impersonating StreamYard was presented as the meeting platform. When the installation appeared to fail, the supposed organizers instructed me to run a Terminal-based installer on my Mac and grant administrator access.
The sender then asked for my wallet address, saying they would send an NFT gift. Around that time I unlocked MetaMask in Chrome. Unauthorized NFT sales, transfers and cryptocurrency withdrawals followed. I did not knowingly authorize or voluntarily arrange the transactions that removed the listed assets.
My X account was also taken over. The identity behind the invitation is unresolved; an account or displayed name used in the approach does not establish the identity of the attacker.
What the local device review found
The retained technical summary describes a root-level persistent component named “cloudsync” and a fake ChatGPT application. Static analysis identified clipboard-monitoring and browser/wallet-data collection capabilities. These findings describe capabilities, not proof of exactly what was extracted or how the blockchain transactions were signed.
Known malicious components were disabled or removed according to the incident records. Invitation messages, screenshots, transaction records, malware hashes and technical notes were retained privately. This page does not certify the device as clean or publish malware installation instructions.
04 / TIMELINE · UTC
What was reported
Personal wallet incident
A fake podcast invitation and malicious Mac installer preceded unauthorized wallet activity and a social-account takeover, according to my complaint.
Two Ethereum NFT transactions
20 NFTs moved at 14:08:59 UTC (17:08:59 Istanbul), followed by 8 NFTs at 14:12:59 UTC (17:12:59 Istanbul). The local purchase review also cites fulfilled marketplace orders and corresponding payments.
Initial IC3 complaint filed
The incident was reported to the FBI’s Internet Crime Complaint Center (IC3).
Supplemental IC3 complaint filed
The saved supplemental submission identifies all 109 NFTs as stolen in the same incident: 28 Ethereum and 81 Robinhood Chain. It adds to the original report, rather than describing a second theft.
OpenSea restriction update
A retained 9 November recovery note attributes to an OpenSea support response the flagging of 81 additional Robinhood NFTs and disabling purchases, sales and transfers through OpenSea’s services. This is a dated account, not a present-day status check or a chain-wide freeze.
05 / TRANSACTION EVIDENCE
What the records establish
Ethereum · 28 NFTs
The retained local review records outgoing transfers and verified OrderFulfilled/payment logs for the 28 Ethereum assets. This supports their movement and marketplace purchase activity; unauthorized use is my declaration. A receiving wallet does not identify the attacker.
Robinhood Chain · 81 NFTs
The identifiers and three transaction references come from retained OpenSea Sale activity. The owner reports every listed item stolen, but independent receipt and ownership-history verification remains outstanding. The register labels these records separately from the Ethereum log verification.
The evidence CSV also records two additional-wallet native transfers of 0.002213697119451016 ETH and 0.000832627798521139 ETH on 31 October, both to the same recipient in the original wallet’s fund trail. These are currency transfers, not two extra NFTs, and not a complete loss valuation. Possible losses on other wallets or networks require further verification.
06 / FBI · IC3 & OPENSEA
FBI/IC3 complaint summary
The original saved IC3 submission is dated 31 October 2026; the saved update is dated 5 November 2026. The submissions describe unauthorized NFT sales/transfers, cryptocurrency withdrawals and a social-account takeover. The update expressly declares all 109 itemized NFTs stolen and requests that the expanded schedule be associated with the original complaint.
The support records describe OpenSea requesting an updated report naming the additional 81 Robinhood assets and confirming the theft declaration. Filing records and a marketplace restriction are different things: neither confirms an FBI investigative finding, recovery of the NFTs or the identity of an offender.
Later buyers, recipients and current holders are not accused of involvement merely because they received or hold an NFT.
How IC3 complaints are handledWhat remains unresolved
The exact signing or credential-theft mechanism, the attacker’s identity, the unitemized part of the overall NFT estimate and possible additional chain losses remain unresolved. The files contain historical ownership/contact checks, not a live ownership register. This page makes no assertion that all assets are currently restricted, that the incident is resolved or that any NFT has been returned.
Help recover the affected NFTs
If you bought a listed NFT or have verifiable recovery information, please contact me through the official Mintropolis account. I would be happy to discuss buying the NFTs back at the price paid in the incident purchases. Later buyers may have been unaware of the theft; please do not harass anyone.
No wallet connection, recovery fee or seed phrase is needed to read this record or contact me. I will not ask for your recovery phrase.